

Trust
Esta página aún no está disponible en tu idioma.
Last reviewed: 8 October 2026
This page is for security and procurement reviewers, Slack app review, and anyone evaluating John CEO before handing him real accounts. It summarizes how the service is built and the commitments we already make. If anything here differs from the Privacy Policy or the Terms of Service, those documents control.
Every section has its own link, so you can point a questionnaire answer straight at it.
Architecture
Section titled “Architecture”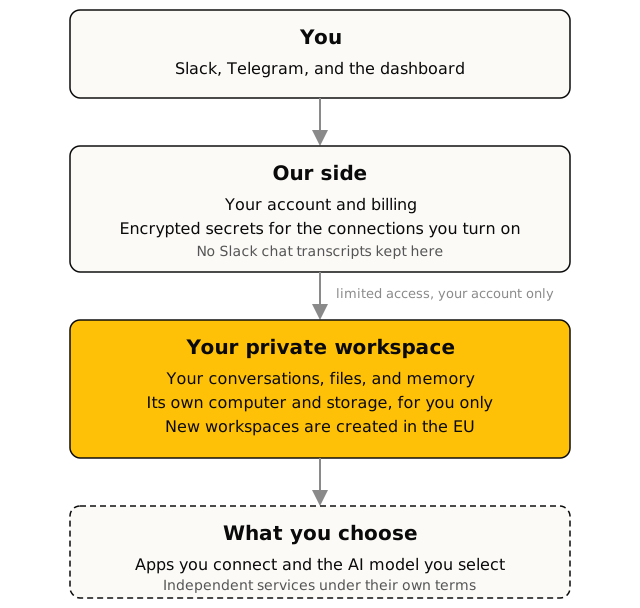
Where you talk to John. Slack for your team, Telegram for you, plus the dashboard. When John works on a request, the message is handled in your private workspace.
Our side. Your account, billing, and encrypted secrets such as your Slack and Telegram keys. The platform secrets that run the service never reach your workspace. Your workspace receives only what your own account needs, such as your AI access key and, if you use Telegram, your Telegram bot’s key. John gets limited access to your accounts only, for the work you ask him to do. We do not keep your Slack chat transcripts. Short-lived routing data exists only so replies land in the right thread.
Your private workspace. Your conversations, files, and memory live in a space set up just for you, on its own computer with its own storage. It is never mixed with another customer’s data. New workspaces are created in the EU. A workspace created before that change keeps its original location until it is recreated.
What you choose. The apps you connect (mail, calendar, CRM, and others) and the AI model you select are independent services under their own terms. They are not our subprocessors for those choices. If the model you select processes content outside the European Economic Area, your selection is your instruction to send the relevant content there.
Public apps. Sites John builds for you on *.johnceo.app are public by design and separate from your private workspace. See Apps.
More detail: Security, Private workspace, Memory.
Subprocessors
Section titled “Subprocessors”The live list at john.ceo/subprocessors is the authority. If this summary and the live list ever differ, the live list is correct. Grouped by job, as of 20 August 2026:
| Job | Provider | Region |
|---|---|---|
| Private workspace and public app files | Hetzner | Global (new workspaces in the EU) |
| Hosting for our side of the service and the admin console | Heroku | EU (Ireland) |
| Database for account and service records | CloudClusters | EU |
| Edge network, security, AI request gateway, inbound email routing, and public app delivery | Cloudflare | Global edge |
| Root key protecting stored connection secrets (no customer content is sent) | Amazon Web Services (KMS) | EU (Ireland) |
| Routing AI requests to the model you select | AI routing provider (named in the live list) | Global |
| Running the connections you authorize | Connection provider (named in the live list) | Global |
| Messaging channels | Slack, Telegram | Global |
| Card payments, tax, and invoicing | Stripe | Global |
| Transactional and workspace email | EmailLabs | EU |
| Error monitoring | Sentry | EU |
| Website analytics, only after you accept cookies | Google Analytics, Microsoft Clarity | Global |
The apps you connect and the AI model providers you select are not on this list. They are services you authorize or choose, under their own terms.
Roles. JHELY GLOBAL SL, established in Spain, is the controller for your account data: registration, billing, and settings. For personal data John reads in the tools you connect, including data about third parties, you are the controller and we act as your processor, on your instructions only.
Data processing agreement. Where you need one under Article 28 GDPR, we make one available on request. Email [email protected].
Legal bases. Performance of our contract with you; our legitimate interests in operating, securing, and improving the service; your consent for non-essential cookies, marketing, and optional conversation sharing; and legal obligations.
Training. By default we do not use your conversations, prompts, or John’s replies to train or improve models beyond what is needed to run the service for you. Where our providers’ contracts allow it, we require them not to train their general models on your content. Optional conversation sharing, including human review, is off unless you turn it on in Settings, and you can turn it off at any time. It never applies to data received through Slack.
Retention and deletion. When you close your account or make a valid deletion request, we delete your content and workspace from active systems, typically within about 30 days. Encrypted backups age out on their normal rotation, currently about 35 days. Billing records are kept as long as the law requires. There is no in-app button to delete everything today. Ask through Support or [email protected].
International transfers. We are established in Spain. Some processing happens outside the EEA, including AI processing through the model you select. Where data goes to a country without an EU adequacy decision, we rely on safeguards such as the European Commission’s Standard Contractual Clauses.
Your rights. Access, correction, deletion, restriction, objection, portability, and withdrawing consent. Email [email protected]. Requests from people whose data sits in your connected tools (your contacts or clients) go to you as controller, and we help as reasonably required. In Spain the lead supervisory authority is the AEPD (aepd.es). Elsewhere in the EEA you can contact your local authority.
Slack. We process Slack data only to run John and carry out requests made in Slack. We do not use it to train generalized AI models or for advertising. After you uninstall John or revoke his access, we stop collecting new Slack data and invalidate his Slack access. Full detail: Slack and team chat data.
EU AI Act
Section titled “EU AI Act”John is an AI system, and he says so. This is how we address the transparency rules in Article 50 of Regulation (EU) 2024/1689.
- In Slack, each person gets a notice the first time they interact with John in a workspace: they are interacting with an AI system operated for your business.
- In Telegram, John is set up to open his first conversation with the same notice.
- Messages to other people. Mail from your workspace email address ends, by default, with a note that John’s email assistant sent it on your behalf. That note, and messages John sends through your other connected apps, do not yet state plainly that an AI sent them. If those recipients need to know a message came from an AI, review and label what John sends.
- Keep the notices. Our Terms forbid removing or hiding these notices, or telling John to.
- Your role. Within your business, you are the deployer of John under the AI Act. If you point him at your staff, clients, or other recipients, any additional transparency or labeling those uses require is yours to provide.
- High-risk use is not allowed. Our Terms prohibit using John as, or inside, a high-risk AI system, for example to make hiring, credit, insurance, or eligibility decisions about people without meaningful human review. If you use him that way anyway, the deployer obligations are yours.
- Risky actions ask first. Write actions in connected apps need your approval unless you already allowed that action. See Approvals.
Security
Section titled “Security”- Isolation. One private workspace per customer, never a shared space where customer data mixes.
- In transit. Dashboard and service traffic uses HTTPS/TLS.
- At rest. Your Slack and Telegram secrets and your access key for AI requests are encrypted with AES-256-GCM. Records in our current encryption format are bound to their own customer, so a copy placed in another account will not decrypt. The root key is held in AWS Key Management Service in the EU (Ireland), cannot be exported, and rotates automatically every year. Logins for the other apps you connect are held by the connection provider listed under Subprocessors.
- Internal access. Access to production systems uses role-based controls.
- You hold the off switch. Revoke any connection from the dashboard and John loses that access. You can uninstall John from Slack and disconnect Telegram at any time.
- Payment cards. We block payment card numbers in actions John takes in connected apps.
- Reporting a vulnerability. Email [email protected]. We aim to acknowledge within 48 hours and give a full response within 7 days. Please do not report security issues in public. Our security.txt has the same contact.
Product detail: Security.
What we do not claim
Section titled “What we do not claim”- We do not hold a SOC 2 report or an ISO 27001 certificate today, and we do not publish a penetration test report.
- We have not completed an AI Act conformity assessment, and John is not offered for high-risk use.
- No method of transmission or storage is completely secure, and we cannot guarantee absolute security. You are responsible for keeping your own account secure.
- AI output can be wrong, incomplete, or inappropriate. Review it before you rely on it.
Common review questions
Section titled “Common review questions”Where is our data hosted? New private workspaces, which hold your conversations, files, and memory, are created in the EU. Our side of the service is hosted in the EU (Ireland) with an EU database, behind Cloudflare’s global edge. AI processing happens where the model you select runs, which can be outside the EEA. See Architecture and Subprocessors.
Do you train AI models on our data? Not by default. Optional conversation sharing is off unless you turn it on, and it never covers Slack data. See GDPR.
Who are your subprocessors? See Subprocessors and the live list at john.ceo/subprocessors.
Is a data processing agreement available? Yes, on request at [email protected].
How do we delete our data, and how long does it take? Ask through Support or [email protected]. Content and the workspace are removed from active systems typically within about 30 days, and backups age out in about 35 days. See GDPR.
Can John act without our approval? Risky write actions ask first unless you already allowed them. Tasks you schedule or pre-approve can run without someone reviewing each step in real time. See Approvals.
How will people know they are dealing with an AI? A first-contact notice in Slack and Telegram. Messages John sends to other people do not yet state plainly that an AI sent them, so review and label them where your recipients need to know. See EU AI Act.
Can we revoke access? Yes. Disconnect any app in the dashboard, uninstall John from Slack, or disconnect Telegram.
How do we report a security issue? Email [email protected]. See Security.
Something not covered here? Email [email protected] with your question or questionnaire.
Contact
Section titled “Contact”JHELY GLOBAL SL, Paseo de la Sierra 29, 29018 Málaga, Spain. CIF B67973388. Email [email protected].